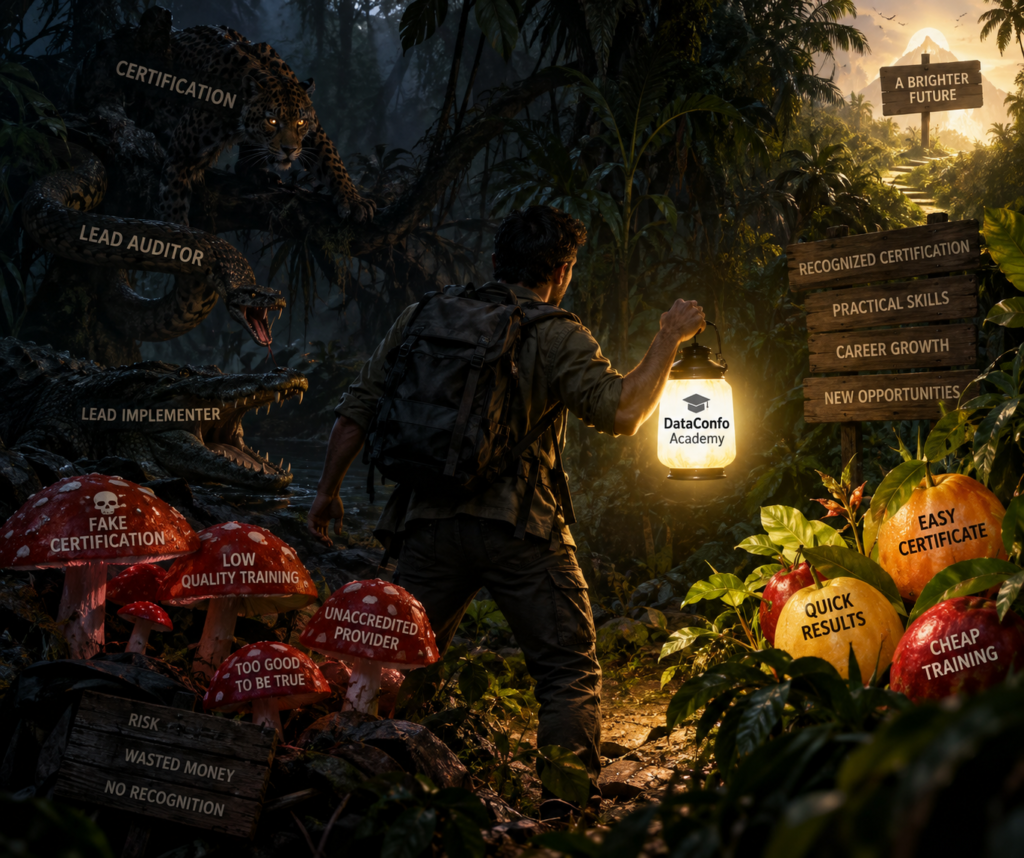
Are you considering an ISO certification to strengthen your CV, develop your expertise, change careers, or start working as a consultant?
You may quickly find yourself facing dozens of options:
ISO Lead Auditor, ISO Lead Implementer, Foundation, Practitioner, e-learning, classroom training, self-study, PECB, CQI and IRCA, and many other providers.
And there is another confusing issue:
Why can one ISO training cost $300 while another costs $1,500 or more?
Are they actually offering the same thing?
Not necessarily.
The price, the training provider’s reputation, and the phrase “internationally recognized certification” are not enough to determine the real value of an ISO certification.
At DataConfo Academy, we believe the right approach is to understand what you are buying, who certifies you, what the certification proves, and how it fits your career objectives.
1. ISO Standard, ISO Training, and ISO Certification: What Is the Difference?
Before comparing prices, you need to understand three different concepts:
the standard, the training, and the certification.
An ISO standard such as ISO/IEC 27001, ISO/IEC 27701, or ISO/IEC 42001 provides requirements or guidance for a management system.
An ISO training course teaches you how to understand, implement, audit, or manage the relevant standard.
A professional certification, on the other hand, is intended to demonstrate that an individual meets defined competency or certification requirements.
These are not the same thing.
For example, ISO 19011 provides guidelines for auditing management systems. It is an auditing guideline, not itself a professional certification for individuals.
So the first question you should always ask is:
What exactly am I receiving at the end of this course?
2. Why Are ISO Training Prices So Different?
You may find an ISO 27001 Lead Auditor course for a few hundred dollars and another one costing more than $1,500.
This does not automatically mean that the cheaper course is bad or that the more expensive one is better.
There are several reasons for the price difference.
The type of certification
A certificate of attendance is not equivalent to a professional certification issued under a formal certification scheme.
Before registering, determine exactly what you will receive:
Certificate of Attendance?
Certificate of Completion?
Foundation Certificate?
Professional Certification?
Lead Auditor or Lead Implementer certification?
The word certificate alone tells you very little.
Accreditation
Accreditation is one of the most important elements to investigate.
For personnel certification, ISO/IEC 17024 establishes internationally recognized requirements for organizations that certify people.
For example, PECB currently states that it is accredited as a personnel certification body by IAS, UKAS, and COFRAC under ISO/IEC 17024.
But don’t stop at the logo.
Ask:
Who provides the training?
Who actually issues the certification?
Which accreditation covers the certification?
What is the scope of that accreditation?
These questions matter more than the marketing slogan.
3. What Really Determines the Price of an ISO Certification?
Several factors can affect the price:
Training format — classroom, live online, e-learning, or self-study.
Duration — one day, several days, or a complete professional pathway.
Trainer expertise — experience, qualifications, and teaching capability.
Examination — whether an exam is included and how it is administered.
Certification process — application, evaluation, experience requirements, and certification issuance.
Study materials — course manuals, exercises, case studies, mock exams, and other resources.
Additional services — mentoring, coaching, consulting sessions, or post-training support.
This is why comparing two training offers simply by their headline price can be misleading.
You need to compare what is included and what qualification you actually obtain.
4. How Can You Tell Whether an ISO Certification Is Legitimate and Valuable?
Don’t choose a certification simply because the provider’s website looks professional.
Use this checklist.
1. Who issues the certification?
Identify the legal entity responsible for issuing it.
2. Is it a training certificate or a professional certification?
These are not interchangeable.
3. Is the certification body accredited?
Look for verifiable accreditation where applicable.
4. Who is the accreditation body?
Don’t stop at the word “accredited.”
Find out accredited by whom.
5. What exactly does the accreditation cover?
Look at the certification body’s scope of accreditation.
6. Is there a formal examination?
Understand how the candidate is assessed.
7. Are there experience requirements?
Some professional certification levels require documented professional experience.
This simple verification process can prevent a common mistake:
comparing prices instead of comparing the qualification you will actually obtain.
5. Which ISO Certification Provider Should You Choose?
There is no single certification provider that is automatically the best choice for every professional.
Your choice should depend on your objective, your target market, and the type of certification you need.
For example, PECB offers professional training and certification schemes across multiple ISO-related areas, while CQI and IRCA operates an approved training partner model for its certified auditor training.
The right comparison is therefore not:
“Which provider is cheapest?”
It is:
Which provider offers the right certification, under what certification scheme, with what accreditation, assessment process, and professional value?
Reputation matters.
Accreditation matters.
But most importantly, the certification needs to match your professional objective.
6. ISO Lead Auditor vs Lead Implementer: What Is the Difference?
This is one of the most important choices you will make.
Lead Auditor and Lead Implementer are not simply two different names for the same course.
They develop different professional perspectives.
7. What Is an ISO Lead Implementer Certification?
A Lead Implementer pathway is particularly relevant if you want to help organizations design, implement, maintain, and improve a management system.
It can be suitable for professionals who want to:
- implement an ISO management system;
- support organizations during certification projects;
- develop policies and procedures;
- perform risk assessments;
- implement controls;
- manage compliance projects;
- prepare organizations for certification audits.
For example:
ISO/IEC 27001 Lead Implementer focuses on implementing an Information Security Management System.
ISO/IEC 27701 Lead Implementer focuses on implementing a Privacy Information Management System.
For consultants, compliance professionals, project managers, and management-system professionals, the Lead Implementer pathway can be particularly relevant.
8. What Is an ISO Lead Auditor Certification?
A Lead Auditor pathway focuses more heavily on auditing and evaluating management systems.
It can be relevant for professionals who want to:
- perform internal audits;
- audit suppliers;
- participate in certification audits;
- work in conformity assessment;
- develop an auditing career;
- evaluate the effectiveness of management systems.
The difference can be simplified as:
Lead Implementer → How do I build and implement the system?
Lead Auditor → How do I assess and audit the system?
Both skill sets can be valuable, and in some careers they complement each other.
9. Should I Choose Lead Auditor or Lead Implementer?
There is no universal answer.
The right choice depends on the job or business model you are targeting.
| Career objective | Potentially relevant pathway |
|---|---|
| ISO Consultant | Lead Implementer |
| Compliance Manager | Lead Implementer |
| Management System Manager | Lead Implementer |
| Cybersecurity Consultant | Lead Implementer / Lead Auditor |
| Internal Auditor | Lead Auditor |
| Certification Auditor | Lead Auditor |
| Audit Firm Professional | Lead Auditor |
| Independent Consultant | Both can be complementary |
| Complete Beginner | Foundation before an advanced specialization |
The biggest mistake is collecting certifications without a professional strategy.
A certification should strengthen your professional positioning, not simply make your CV longer.
10. Are ISO Certifications Still in Demand?
ISO standards remain widely used by organizations to structure management systems and address the expectations of customers, business partners, regulators, procurement processes, and other stakeholders.
But not every ISO standard offers the same professional opportunity.
The most interesting choice depends on where business and regulatory needs are developing.
For professionals working in information security, privacy, AI governance, compliance, risk management, and digital transformation, several standards are particularly worth watching.
11. ISO/IEC 27001, ISO/IEC 27701, and ISO/IEC 42001: Which One Should You Consider?
ISO/IEC 27001
ISO/IEC 27001:2022 specifies requirements for an Information Security Management System (ISMS). ISO describes it as a framework for managing information-security risks and protecting the confidentiality, integrity, and availability of information.
It is particularly relevant to professionals working in:
information security, cybersecurity, IT governance, risk management, and compliance.
ISO/IEC 27701
There is an important update here that candidates should know about.
ISO/IEC 27701:2025 is now the current edition, replacing the 2019 edition. It specifies requirements and guidance for a Privacy Information Management System (PIMS) and applies to organizations acting as controllers and processors of personally identifiable information.
It can be particularly relevant to:
DPOs, privacy professionals, data protection consultants, compliance professionals, and privacy governance specialists.
ISO/IEC 42001
ISO/IEC 42001:2023 specifies requirements for an Artificial Intelligence Management System (AIMS).
ISO describes it as the world’s first AI management system standard, providing a structured framework for organizations developing, providing, or using AI systems.
This makes it particularly interesting for professionals working in:
AI governance, AI compliance, responsible AI, risk management, and AI management systems.
The strategic question is therefore not simply:
“Which ISO certification is the most famous?”
It is:
“Which ISO standard addresses the problems organizations are increasingly required to manage?”
12. Does an ISO Certification Guarantee a Job?
No.
And this is important to understand before investing in any certification.
A professional certification can strengthen:
your credibility, knowledge, CV, professional network, and access to certain opportunities.
But it does not replace:
experience, practical skills, professional judgment, and proven results.
A consultant with three relevant certifications and several successful projects may be more valuable than someone with ten certifications and no practical experience.
The strongest profile is usually:
Certification + Expertise + Experience + Demonstrable Results
13. Which ISO Training Should a Beginner Choose?
You don’t necessarily need to start with a Lead Auditor or Lead Implementer course.
Start by determining three things.
Where am I today?
Are you a complete beginner, an experienced professional, or already working in the relevant field?
What role do I want?
Consultant?
Auditor?
Compliance Manager?
DPO?
Information Security Manager?
AI Governance Professional?
What skill do I actually need?
Do you need to understand the standard?
Implement it?
Or audit it?
For beginners, a Foundation course can provide a useful introduction.
For professionals who want to implement management systems, Lead Implementer may be more appropriate.
For professionals targeting auditing, Lead Auditor may be the better direction.
14. Be Careful With “Cheap ISO Certifications”
A low price does not automatically mean low quality.
A low-cost e-learning or Foundation course can be perfectly legitimate and useful.
The problem occurs when marketing suggests that a simple attendance certificate is equivalent to a professionally certified and accredited qualification.
Before paying, verify:
the certification body, accreditation, accreditation scope, examination, prerequisites, certification requirements, and the exact certificate you will receive.
The important question is not:
“How much does it cost?”
It is:
“What am I getting for that price?”
15. The DataConfo Academy Checklist Before You Buy an ISO Certification
Before registering for an ISO certification course, ask yourself these 10 questions:
1. Which ISO standard will I study?
2. What certification level will I obtain?
3. Am I buying training or professional certification?
4. Who issues the certificate?
5. Is the certification body accredited?
6. Which accreditation covers the certification?
7. Is there a formal examination?
8. Are professional experience requirements involved?
9. Does this certification match my target career?
10. What is the expected professional return on investment?
If you cannot answer these questions clearly, don’t pay yet.
16. Don’t Just Choose a Certification. Build a Professional Profile.
The market is not simply looking for people who can say:
“I am ISO 27001 certified.”
Organizations need professionals who can say:
“I can assess your current situation, identify your risks, design the appropriate management framework, support implementation, and prepare you for audit.”
That is a completely different value proposition.
A certification provides structured evidence of knowledge and competence.
Your professional experience provides evidence that you can apply that knowledge in the real world.
Conclusion: Which ISO Certification Should You Choose?
There is no universally “best” ISO certification.
The right choice depends on:
your professional background, your industry, your career objective, the market you want to serve, and the skills you want to monetize.
Before choosing, evaluate:
1. Your target role
2. The relevant ISO standard
3. The appropriate certification level
4. The certification provider
5. Accreditation
6. Examination and certification requirements
7. Your expected professional ROI
And remember:
Higher price ≠ better certification
Lower price ≠ poor certification
The real question is:
What does this certification actually prove, who issues it, under what framework, and how valuable will it be for my professional career?
At DataConfo Academy, our objective is to help professionals make informed decisions about ISO standards, professional certifications, Lead Auditor and Lead Implementer pathways, based on a real career strategy rather than simply a logo or a price tag.